Announcing AI-Native Market Access Product for Regulated Products

Learn More

Blogs

MedTech

Competent Authority, Notified Body, Authorized Representative – who’s who and what do they do?

By

Bethaney Lentz

August 2, 2023

4 min read

Marketing medical devices in the European Economic Area (EEA) can be a challenge as manufacturers must navigate changing regulations, and an array of agencies across the region and in specific countries. Some regulatory activities require interactions with regional level authorities, while others are handled by Member States, and it’s not always clear when to engage with which authority.

This article explains the different regulatory bodies that oversee medtech products within the European region, their roles in the market clearance processes, and a full list of relevant country-specific authorities.

Competent Authorities

A Competent Authority belongs to the government of a Member State of the European Union (EU) and is responsible for transposing the requirements of European regulations into national legislation. There is an umbrella group called the Competent Authorities for Medical Devices (CAMD) that is responsible for improving communication and collaborative work between these competent authorities, and increasing the surveillance of medical devices on the market. All of the competent authorities work together in the CAMD network to support patient safety and organize the implementation and the enforcement of the regulations on medical devices and in vitro diagnostic devices.

Notified Bodies

Medical devices are initially reviewed and approved by a Notified Body before they are placed on the market. Notified Bodies are supervised by the Competent Authority of a particular EU Member State. A Notified Body is an independent organization designated by an EU Member State to make sure that the Medical Device Requirements (MDR) and In Vitro Diagnostic Requirements (IVDR) are being followed for as long as the product remains on the market. Notified Bodies are also designated for specific directives, regulations, or products that need higher and stricter safety standards, or those that weren’t built according to harmonized EN standards, such as electronic equipment, gas appliances, and certain medical devices.

A medical device that has been approved for the market will bear a “CE mark” which indicates that it meets the basic requirements for safety and effectiveness under European law. In addition, The Commission assigns a 4-digit code to each Notified Body, with the purpose of uniquely identifying each company that acts as a Notified Body. The codes range from 0001-2900, and they must be placed below the CE Mark on the product and/or it’s packaging, and on the user manual.
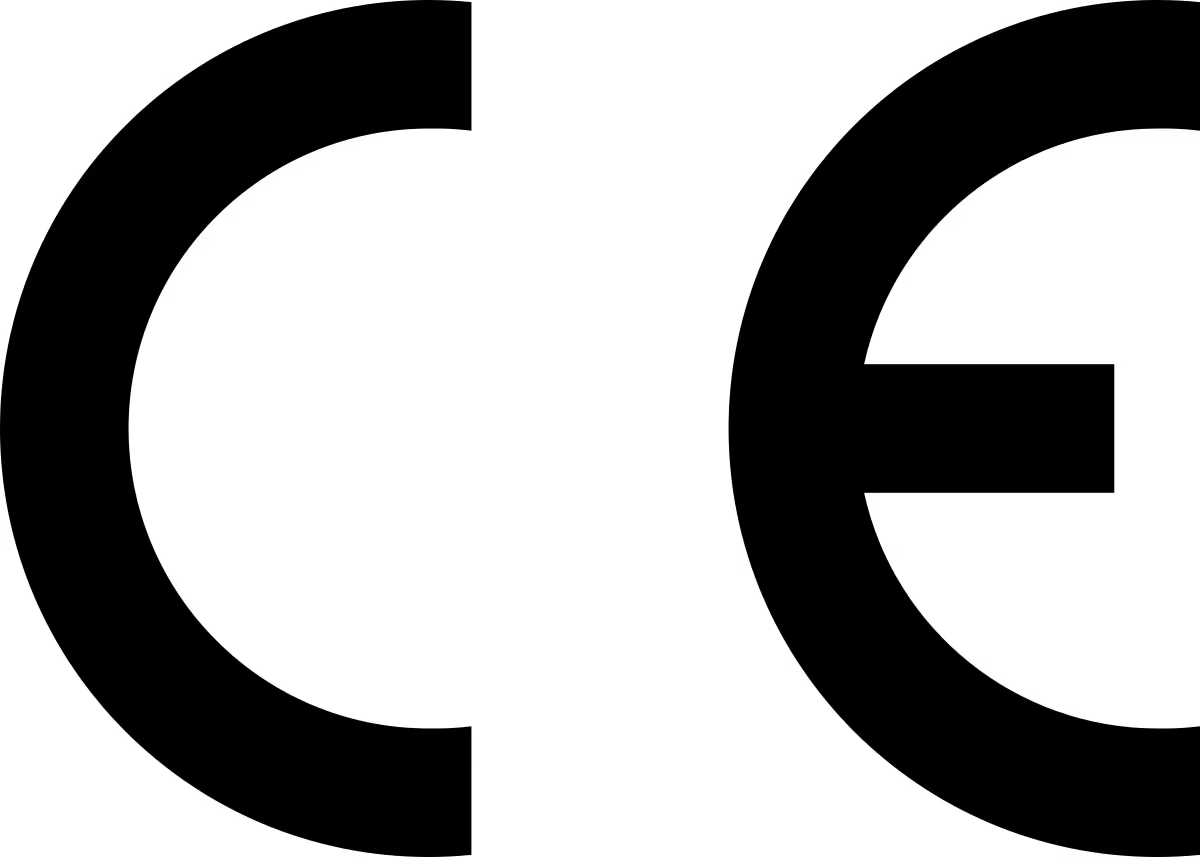
CE Mark
CE mark example

Authorized Representatives

According to EU directive 2017/745 and 2017/746, it is a legal requirement to appoint a European Authorized Representative (EU Rep) for a medical device manufacturer who does not have a registered place of business in a particular EU Member State. This role will be the liaison between the manufacturer and the Competent Authority. The name and address of the EU Rep must be included on the labelling, outer packaging or on the instructions for use as designated in EN ISO 15223-1:2021

Generally speaking, each Member States’ Competent Authority is responsible for monitoring the safety of medical devices after they are placed on the European market. They are given the authority to act on behalf of the government of an individual European Union Member State to ensure that the regulations are being monitored for compliance with the national statutes and regulations according to EU law.

EU National Competent Authorities

A list of contact points for each of the authorities can be found on the European Union website.

Country Competent Authority
Austria Austrian Agency for Health and Food Safety
Belgium Federal Agency for Medicines and Health Products
Bulgaria Bulgarian Drug Agency
Croatia Agency for medicinal products and medical devices of Croatia
Cyprus Cyprus Medical Devices Competent Authority
Czechia Ministry of Health Department of Pharmacy, Medical Devices Unit
Denmark Danish Medicines Agency
Estonia Health Board, Medical Devices Department
Finland Finnish Medicines Agency
France National Agency for the Safety of Medicine and Health Products
Germany Federal Institute for Drugs and Medical Devices
Paul Ehrlich Institute
Greece National Organization for Medicines
Hungary National Institute of Pharmacy and Nutrition
Iceland Icelandic Medicines Agency
Ireland Health Products Regulatory Authority (HPRA)
Italy Ministry of Health, Directorate General of Medical Devices and Pharmaceutical Services
Latvia The States Medicine Agency
Liechtenstein Office of Health / Department of Pharmaceuticals
Lithuania State Medicines Control Agency
Luxembourg Ministry of Health
Malta Medicines Authority
Netherlands Healthcare Inspectorate
Norway Norwegian Medicines Agency
Poland Office for Registration of Medicinal Products, Medical Devices and Biocidal Products
Portugal National Authority of Medicines and Health Products
Romania National Authority of Medicines and Medical Devices
Slovakia State Institute for Drug Control and Medical Devices
Slovenia Agency for Medicinal Products and Medical Devices of the Republic of Slovenia
Spain Spanish Agency for Medicines and Health Products
Sweden Medical Products Agency
Switzerland Swiss Agency for Therapeutic Products, Medical Devices
Turkey Turkish Medicines and Medical Devices Agency, Ministry of Health
United Kingdom Medicines and Healthcare Products Regulatory Agency (MHRA)

Managing regulatory complexity for European submissions and compliance

Deciphering agencies, and understanding when to engage with which authorities is only one of the complexities that medtech regulatory affairs professionals have to deal with. The new MDR and IVDR regulations have introduced new product registration, universal unique device identification (UDI), and standards and evidence requirements. At Rimsys, we’ve authored several ebooks to help regulatory affairs teams navigate these changes. For more information, check out:
Similar posts

AI

Regulatory operations

MedTech

Why Enterprise AI in MedTech Regulatory Is 90% Foundation: The Iceberg Problem

By

James Gianoutsos

November 11, 2026

4 min read

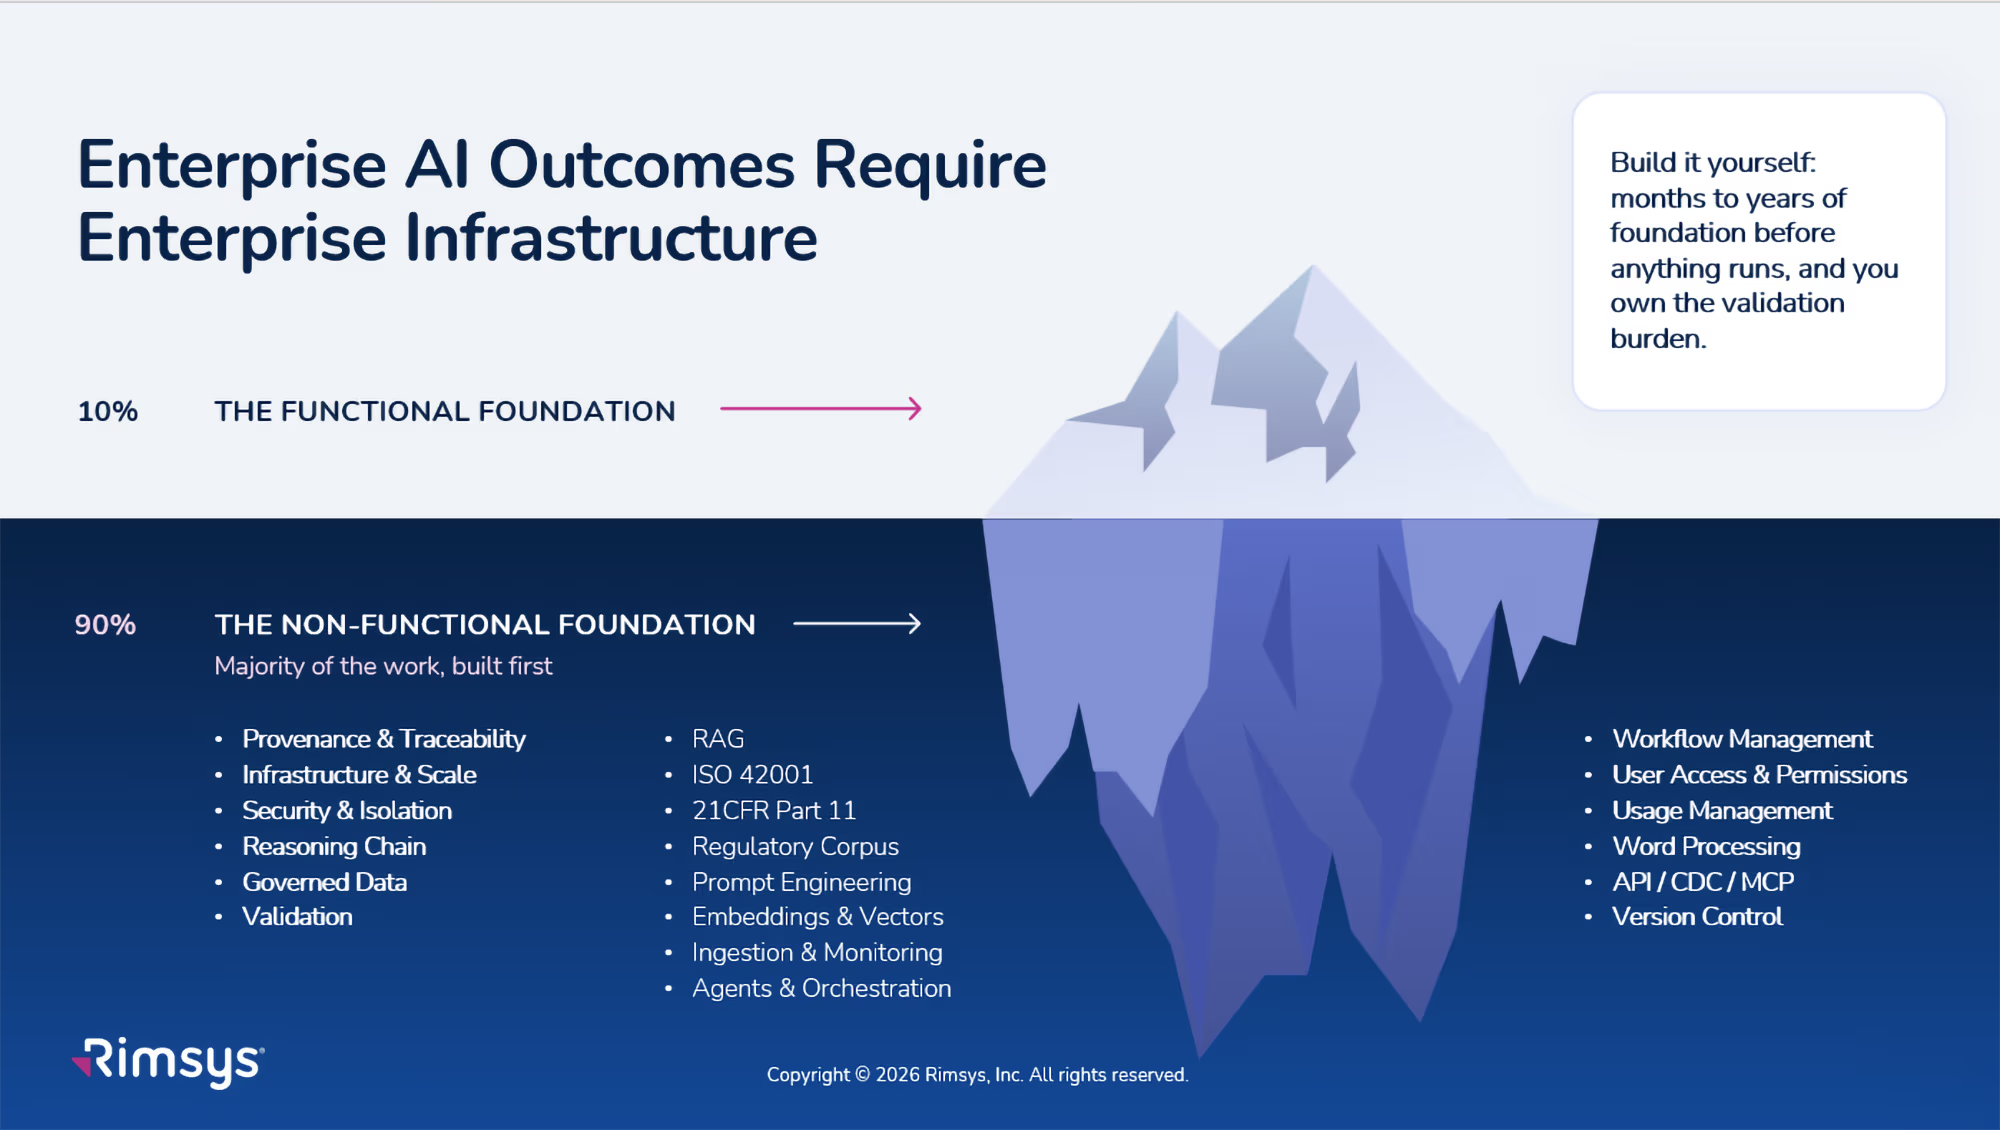
The AI demo is the easy part. In MedTech regulatory operations, the features a team sees in a demo represent roughly 10% of the work required to run enterprise AI. The other 90% sits below the waterline.

Most regulatory leaders have now seen an impressive AI demo. A model drafts a submission summary, answers a question about market requirements, or flags a gap in a technical file. It looks finished. It is not.

What makes AI usable in a regulated environment is everything the demo never shows: the governance, data, and operational foundation that lets a regulatory team trust an output, trace it, and defend it in an audit. That foundation has to be built first, and it is where the real effort lives.

The 10% you can see

The functional layer is what users interact with: the context window, a generated draft, an answer or summary, and maybe a recommendation. It is what vendors showcase and what internal pilots usually build first.

This layer matters. But on its own, it answers only one question: can the model produce something useful? In regulatory work, the harder questions follow immediately. Where did that answer come from? Who approved it? Can we prove it was correct on the day we relied on it? How do we prove it to an auditor? Whatever the answer is, we can all agree it can't be "we stumbled across this Reddit thread."

The functional layer cannot answer any of those hard questions. The foundation underneath it has to, and it has to be trusted and defensible.

Below the waterline: trust and governance

So what does a trusted, defensible foundation look like? It is built from the controls that let a regulatory team stand behind every AI output, because "the model said so" will not hold up with an auditor or a quality system.

  • Provenance and traceability. Every output links back to the source data and documents it drew from.
  • Reasoning chain. Reviewers can see how the system reached a conclusion, not just the conclusion itself.
  • Governed data. The AI works only from controlled, current, approved information.
  • Validation. The system is validated for its intended use, and revalidated as models and data change.
  • Security and isolation. Sensitive product and submission data stays protected and separated.
  • Compliance frameworks. 21 CFR Part 11 for electronic records and signatures, ISO 27001 certification, SOC 2 Type II, ISO/IEC 42001 certification nearing completion, penetration testing, independent audits, and more.

None of these are features a user clicks. All of them determine whether a regulatory team can actually rely on what the AI produces.

Below the waterline: data and intelligence

A general-purpose model does not know your products, your registrations, or the nuances of more than 130 markets. Making it useful for MedTech regulatory work takes a dedicated intelligence layer.

  • Regulatory corpus. A curated, maintained body of regulations, guidance, and requirements by market.
  • Retrieval-augmented generation (RAG). Answers grounded in your own structured data and approved sources, not the model's general training.
  • Embeddings and vectors. The indexing that lets the system find the right record or clause quickly and accurately.
  • Prompt engineering. Tested, controlled instructions tuned to regulatory tasks.
  • Ingestion and monitoring. Pipelines that keep data current and watch for drift or degraded output quality.
  • Agents and orchestration. Coordination of multi-step tasks, with clear checkpoints for human review.

This is where domain specificity is won or lost. Generic AI layered on top of documents produces generic answers. AI built on a structured regulatory data model produces answers that reflect real requirements, country nuances, and product context.

Below the waterline: operations at enterprise scale

Even trustworthy, well-grounded AI fails if it cannot live inside the way regulatory teams actually work. The operational layer turns a capability into a system.

  • Workflow management. AI output flows into review, approval, and change control, not a separate chat window.
  • User access and permissions. The right people see the right data, across regions, partners, and in-country sponsors.
  • Usage management. Visibility into how AI is used, by whom, and at what cost.
  • Version control. A complete history of what changed, when, and why.
  • Word processing. Drafts land where regulatory content is authored and finalized.
  • APIs, change data capture, and MCP. Connections to ERP, PLM, QMS, and the rest of the enterprise stack.
  • Infrastructure and scale. Performance that holds up across the most complex global portfolios.

This is the layer that separates a promising pilot from an operation a global regulatory team can run every day.

The build-it-yourself reality

For organizations considering an in-house build, the iceberg changes the math. The foundation comes first, and it can take months to years before anything useful runs.

The ownership does not end at launch, either. A team that builds its own regulatory AI also owns its validation, its audit defense, and its upkeep as models, regulations, and data evolve. That work lands on the same people who were supposed to be freed up by AI in the first place.

Building is not wrong for every organization. But it should be a deliberate decision made with the full iceberg in view, not just the 10% above the surface.

Five questions to ask before you build or buy

Whether the AI comes from an internal team or a partner, these questions surface what sits below the waterline:

  1. Can every AI output be traced to its source data, with the reasoning visible to a reviewer?
  2. Who validates the system, and what happens to that validation when the model or data changes?
  3. Is the AI grounded in a structured regulatory data model, or layered on top of documents?
  4. Does AI output move into governed workflows, with human review and approval built in?
  5. Is AI something your team can turn on when ready, or is it a prerequisite for using the platform?

If the answers are vague, the foundation probably is too.

Enterprise AI outcomes require enterprise infrastructure

The organizations getting real value from AI in regulatory operations are not the ones with the most impressive demos. They are the ones that invested in the foundation first: governed data, traceable outputs, validated systems, and workflows that keep human judgment firmly in control.

At Rimsys, that foundation is the platform. Rimsys AI runs on the same structured regulatory data model, governed workflows, and enterprise infrastructure that 6 of the top 12 global MedTech manufacturers rely on today. And because not every team is ready for AI at the same time, it is a configuration option: available when you are ready to accelerate, optional when you are not.

Want to see what sits below the waterline? Talk to our team about how Rimsys brings trusted AI to the heart of regulatory operations.

AI

From Regulatory Knowledge to Better Market Decisions: A Conversation with Steve Gens and James Gianoutsos

October 1, 2026

4 min read

AI is moving quickly from experimentation to implementation across life sciences. For regulatory teams, that raises a bigger question than where AI can automate a task:

How can organizations use AI to make better decisions while maintaining the traceability, expert oversight, and confidence regulatory work demands?

That was a central theme when James Gianoutsos, Founder and CEO of Rimsys, joined Steve Gens, Founder and Managing Partner of Gens & Associates, on the Regulatory Executive Podcast.

Their conversation explored the changing role of regulatory intelligence, the introduction of Rimsys Market Access, the importance of transparency in regulatory AI, and what these changes could mean for regulatory teams.

Regulatory knowledge has been difficult and costly to scale

For global medtech organizations, regulatory knowledge has traditionally been highly dependent on people.

A company may have specialists responsible for particular countries or regions, along with local representatives, distributors, consultants, and other experts. Those people develop deep knowledge of local regulations, pathways, and expectations.

The problem is that the knowledge often remains distributed across the organization. And maintaining that market-by-market expertise can become expensive as a company expands its portfolio and geographic footprint.

As James described during the podcast, large manufacturers may rely on dozens or even hundreds of internal employees, third-party distributors, local representatives, and other specialists to understand what it takes to bring products into different markets. Smaller organizations may rely more heavily on outside consultants and partners. Either way, the model can be costly and difficult to scale. 

But the cost isn't limited to what companies spend on expertise.

Steve described the workflow as a series of “start, stop” cycles: ask a local expert, verify whether the regulation is current, gather more information, and repeat. Each cycle consumes regulatory capacity and extends the time it takes to give the business a confident answer.

That creates another potentially more consequential expense: the cost of waiting.

When it takes months to understand what entering a market will require, commercial and product teams have less visibility into when revenue might begin, what resources will be needed, or whether the opportunity is worth pursuing. Regulatory teams spend valuable capacity assembling and validating information rather than applying their expertise to more strategic work.

Ultimately, scaling regulatory knowledge isn't simply an efficiency problem. It affects how quickly and confidently the business can decide where to invest.

The bigger question: Should we enter this market?

That challenge is central to Rimsys Market Access.

Most market-entry research begins with questions such as: How is the product classified? What's the regulatory pathway? What are the requirements?

Those questions establish whether a company can enter a market. But they don't necessarily tell the business whether it should.

Market Access is designed to help regulatory and commercial teams develop an earlier view of what market entry could involve, including classification, regulatory pathway, timeline, cost considerations, requirements and potential gaps. 

For commercial and product leaders, that provides greater predictability before committing budget and resources.

For regulatory leaders, it means starting with a structured plan rather than assembling every market assessment from scratch.

Moving regulatory knowledge from individuals into a shared system

During the conversation, James described one of AI's most significant opportunities as moving knowledge that has historically lived in people's heads into software.

The goal isn't to eliminate regulatory expertise. It's to make that expertise more scalable.

Market Access works from a curated regulatory corpus, allowing market-specific knowledge to be applied across workflows without requiring every initial question to go through the individual who happens to know that jurisdiction. Outputs are designed to trace back to the underlying regulation, guidance, or law. 

That can also change where regulatory professionals spend their time. Rather than focusing as heavily on finding information and assembling initial assessments, they can focus on reviewing the evidence, identifying gaps, applying judgment, and advising the business.

Steve described the concept as a subject-matter-expert assistant. James called it a workforce multiplier. 

Trust requires opening the regulatory AI “black box”

Speed isn't enough when the information is being used to inform regulatory decisions.

James and Steve returned repeatedly to the importance of knowing where an AI-generated answer comes from. As Steve summarized it during the discussion, transparency builds trust.

Market Access is designed around that principle. Its outputs are grounded in a curated regulatory corpus and traceable to the specific regulations, guidance, or laws supporting them. That gives regulatory professionals the ability to verify an answer rather than simply accept it. 

Human judgment remains essential as well. Market Access provides an upfront assessment, not a guarantee of a regulatory outcome. Reviewer interpretation and other factors can still affect what happens during the regulatory process.

The objective isn't to make uncertainty disappear. It's to make what is known, what the sources say, and where uncertainty remains much easier to see.

Connecting the market decision to execution

The discussion also pointed to a broader evolution in regulatory technology: moving from systems that primarily store regulatory information toward systems that help teams act on it.

That's where Market Access and Rimsys RIM play distinct but complementary roles.

Market Access is the planning layer. It helps teams determine whether, when, and how to enter a market.

Rimsys RIM is the execution layer. It manages the registrations, submissions, regulatory changes, and ongoing regulatory work required to act on that plan. 

Together, they create a path from the initial market decision through regulatory execution rather than leaving planning and execution disconnected.

A new role for AI in regulatory work

One of the most interesting themes from Steve and James's conversation was that AI's impact may ultimately be less about replacing individual tasks and more about expanding what regulatory teams can accomplish.

Better access to market-specific knowledge can help professionals work across more markets, spend less time gathering information, and devote more capacity to the judgment and strategic work that requires their expertise.

The technology is changing quickly, but the fundamentals of regulatory work remain: reliable information, domain expertise, transparency, and human judgment.

The opportunity is to apply those fundamentals at greater scale while giving the business a clearer answer to the question that comes before execution:

Not simply, “Can we enter this market?”

But, “Should we?”

Listen to the full conversation

Hear the complete discussion between Steve Gens, Founder and Managing Partner of Gens & Associates, and James Gianoutsos, Founder and CEO of Rimsys, on the Regulatory Executive Podcast for more on regulatory AI, market-entry planning, transparency, and the changing role of regulatory teams.

‍

AI

How Market Access Builds Trust in Regulatory Intelligence

By

Bethaney Lentz

September 18, 2026

4 min read

Why source traceability, regulatory specificity, and human judgment matter when AI informs a market-entry decision.

Regulatory professionals are not short on AI options. General-purpose tools can answer questions quickly and often sound convincing. But in medtech, a convincing answer is not the same thing as a decision you can defend.

That distinction matters most before a company commits to a new market. Teams need to understand how a product is classified, which pathway applies, how long entry may take, what it may cost, where the important gaps are, and what uncertainty still remains. Commercial leaders need that visibility to decide whether the opportunity is worth pursuing. Regulatory leaders need to know that the assessment is grounded in sources they can verify.

That is the trust standard behind Rimsys Market Access. It is not simply about producing regulatory information faster. It is about helping medtech teams decide whether, when, and how to enter a market before committing budget and resources, with outputs linked back to the regulations, guidance, and laws behind them.

Why fluency is not enough for regulatory work

A general AI tool can be useful for brainstorming, summarizing, and exploring a topic. The challenge comes when an answer has real regulatory consequences. A plausible response may still be incomplete, based on the wrong designation, or disconnected from the current source that should govern the decision.

Medtech makes this especially difficult because the same product can be treated differently across markets and product designations. Medical device, IVD, cosmetic, consumer, OTC, and combination-product considerations can change the regulatory read. A market-entry assessment has to account for that context rather than assume one answer travels cleanly from one jurisdiction to another.

For regulatory teams, the natural next question is: Where did this answer come from? If the system cannot show the underlying authority, the expert still has to rebuild the research before trusting the result. That limits the value of the speed AI was supposed to create in the first place.

Trust starts with a decision you can verify

Market Access is designed around a different outcome. The goal is not to give teams another stream of regulatory information to interpret. It is to provide a source-linked market plan that helps them answer the bigger business question: should we enter this market, not just can we?

For a market assessment, that can include classification, regulatory pathway, timeline, cost considerations, key requirements and potential gaps. The output is designed to give commercial and product leaders an earlier, more defensible view of the opportunity while giving regulatory professionals the detail they need to review the basis for the assessment.

Trust comes from being able to inspect that basis. Market Access works from a curated regulatory corpus spanning more than 200 markets rather than relying on the open web. Answers are linked to the specific regulation, guidance, or law behind them, so a regulatory professional can verify the source instead of being asked to accept an AI-generated conclusion on faith.

Three things make regulatory intelligence more defensible

1. Source traceability

A regulatory answer is more useful when the person reviewing it can follow the evidence. Market Access links outputs back to their underlying regulatory sources. That changes the review process from “Do I trust the AI?” to a more practical question: “Does the cited source support this conclusion for our product and situation?”

That is an important shift for regulatory teams. Instead of assembling every market assessment from a blank page, they can review a structured, sourced plan, challenge assumptions, and focus their expertise on the places where judgment matters most.

2. Regulatory specificity

Trust also depends on context. Market Access is purpose-built for medtech regulatory complexity and supports cross-designation classification. The objective is to evaluate the product in the context of the market and the applicable regulatory framework, then carry that context into the pathway, requirements, timeline, cost considerations, and gaps that shape the market-entry decision.

This is where a purpose-built market-planning platform differs from a generic chat experience. The value is not an impressive answer in isolation. It is a connected assessment that helps the team understand what entering the market is likely to require and whether the opportunity still makes sense once those requirements are visible.

3. Human judgment stays in control

No system can remove every area of uncertainty from regulatory work. Reviewer interpretation and expert judgment still affect outcomes, and Market Access is not designed to promise approval.

Instead, Market Access is designed to make uncertainty more manageable. Regulatory professionals review and validate the work before it moves into execution. They can verify sources, assess the gaps, and apply company and product context that software cannot fully replace. The technology accelerates the research and planning. The regulatory professional remains responsible for the judgment.

What trust looks like in a market-entry decision

Imagine a team evaluating several markets for a new product. The commercial question is not simply whether registration is technically possible. The team needs to know which markets deserve investment now, which may require more evidence or resources, and which could put the revenue window at risk because the pathway is longer or more complex than expected.

Regulatory has a different, but connected, need. They have to understand the classification and pathway, identify the requirements most likely to slow the submission, and confirm that the plan reflects the relevant regulatory sources.

Market Access brings those views together. Commercial and product leaders get earlier visibility into timing, cost considerations, requirements, and risk so they can build a stronger business case. Regulatory teams get a source-linked plan they can review rather than a collection of unsupported conclusions. Both groups are working from the same market-entry picture before significant resources are committed.

Trust is not the end goal. Better decisions are.

It is easy for a conversation about regulatory AI to become a conversation about models, agents, or architecture. Those details matter, but they are not the business outcome.

The real value of trustworthy regulatory intelligence is what it lets a team do next. It can help a commercial leader defend a market investment. It can help regulatory surface issues earlier. It can give both groups a more predictable view of the work ahead before budget, R&D capacity, or launch timing is locked in.

And once the decision is made, the work does not have to stop at an intelligence report. Market Access is the market-planning layer. Rimsys RIM is the execution layer for registrations, submissions, regulatory changes, and ongoing regulatory work. Each can stand on its own, and together they create a path from the market-entry decision into controlled execution.

A more useful standard for regulatory AI

The question for medtech teams should not be whether AI can produce a regulatory answer. It can. The better question is whether that answer is specific enough, traceable enough, and reviewable enough to support a real decision.

Market Access is built around that standard: a defensible view of whether, when, and how to enter a market, grounded in curated regulatory sources and kept under human review. Because when the decision affects revenue, resources, and regulatory strategy, sounding right is not enough. Teams need to see why the answer is right, where uncertainty remains, and what it means for the decision in front of them.

I agree to the privacy policy including to Rimsys using my contact details to contact me for marketing purposes.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Hand holding smartphone showing email app with 12 unread messages notification.