The beginner's guide to the FDA De Novo classification process
This article is an excerpt from The beginner's guide to the FDA De Novo classification process ebook.
Contents
- Introduction
- Chapter 1: What is an FDA De Novo request?
- Chapter 2: Contents of a De Novo request
- Chapter 3: Submitting a De Novo request
- Appendix A: Acceptance review checklist
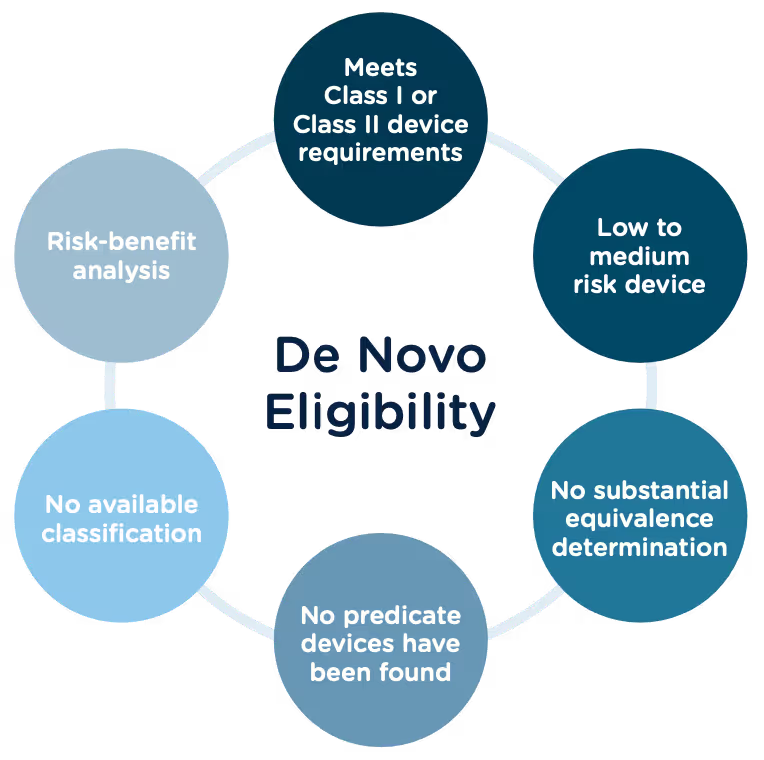
Congratulations, you have successfully developed a new medical device! Now you need to take it to market. Normally in the United States this would mean completing a 510(k) submission. However, the 510(k) relies on “substantial equivalence”—a comparison to a similar device already on the market (also called a predicate device) to assess the risk profile of the new device. What if your device is totally new, and there isn’t a similar device to compare it to? Enter the FDA De Novo process. The De Novo process provides a pathway to market for novel devices with a low to medium risk profile.
What does De Novo mean?
According to the Merriman-Webster dictionary, de novo is a Latin word meaning “as if for the first time; or anew.” Perfectly fitting that the FDA uses this term “De Novo” to describe market approval requests for new medical devices or technology where there is no comparable predicate device on the market.
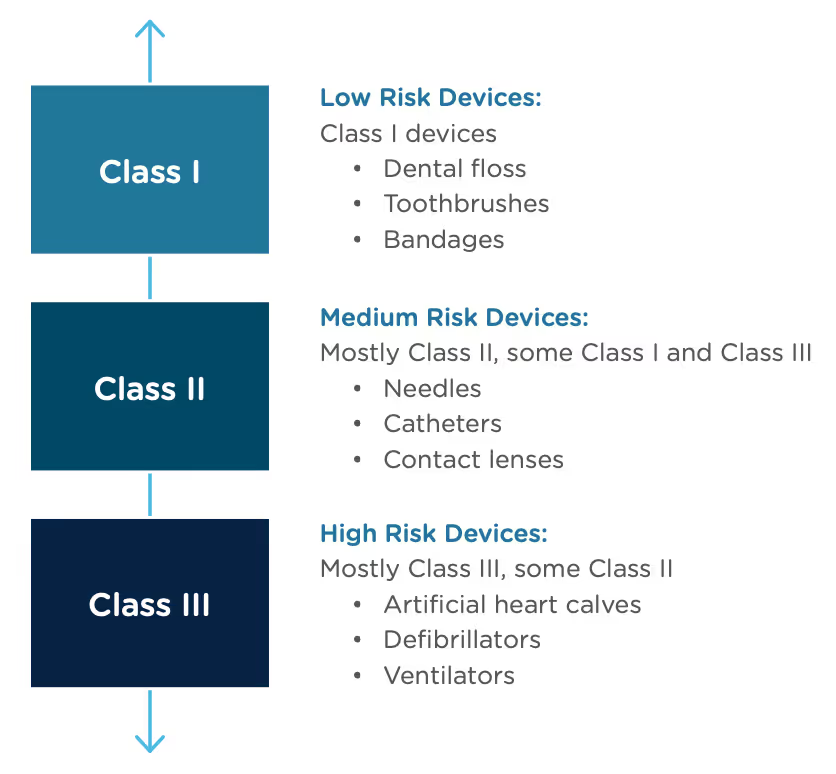
The Food and Drug Administration Modernization Act of 1996 provided the FDA with the authority to create the De Novo Classification Process. It's a process that uses a risk-based strategy for a new, novel kind of medical device, in vitro diagnostic, or medical software solution whose type has previously not been identified and/or classified. It’s a process by which a novel medical device can be classified as a Class I or Class II device, instead of being automatically classified as Class III, which may not be appropriate. Before the implementation of the De Novo process in 1997, all the “not substantially equivalent” (NSE) products were required to be initially classified as a Class III device. But for a lot of devices, this risk class didn’t really make sense. The De Novo process provides a pathway for more accurate classifications of novel, lower-risk devices.
October, 2021, the FDA released a final guidance document "De Novo Classification Process (Evaluation of Automatic Class III Designation)" to provide guidance to the requester (also known as the manufacturer) and the FDA on the process for the submission and review of a De Novo Classification Request under section 513(f)(2) of the Federal Food, Drug, and Cosmetic Act (the FD&C Act). This process provides a pathway to an initial Class I or Class II risk classification for medical devices for which general controls or general and special controls, provide a reasonable assurance of safety and effectiveness, but for which there is no legally marketed predicate device. This guidance document replaced the "New Section 513(f)(2) – Evaluation of Automatic Class III Designation, Guidance for Industry and CDRH Staff" document, dated February 19, 1998.
Consistent with the final rule, the FDA updated the guidance documents below to provide recommendations for submitting De Novo requests, as well as criteria and procedures for accepting, withdrawing, reviewing, and making decisions on De Novo requests, effective January 3, 2022.
- User Fees and Refunds for De Novo Classification Requests
- FDA and Industry Actions on De Novo Classification Requests: Effect on FDA Review clock and Goals
- Acceptance Review for De Novo Classification Requests
The 510(k) and the De Novo processes are similar in that they are both pathways to market for medical devices with low to moderate risk, which is Class I and Class II. The biggest difference between the two is that the 510(k) heavily relies on the concept of "substantial equivalence" to an existing medical device. You must prove this to get the clearance of your 510(k) submission. In the De Novo process, there isn’t a product currently on the market that is “substantially equivalent” to yours, so it’s like starting with a clean slate. For more on the 510(k) process, see our Beginner’s Guide to the 510(k) ebook.
A result of the De Novo process to be aware of is that a successful submission will lead to a new predicate device type that someone else can reference to bring their product to market through the 510(k) process. You’ve done all the work, so now it’s available for anyone to use to provide "substantial equivalence".
De Novo history/timeline
Preparing a De Novo request
1. Do your research! Be sure to complete all the necessary research prior to your submission. You want to be sure that your device is not substantially equivalent to an existing device. Resources to review include:
- The Center for Devices and Radiological Health (CDRH)
- U.S. FDA Device Classification Database
- Device Classification Under Section 513(f)(2)(De Novo)
2. A De Novo request can be submitted with or without a preceding 510(k). There are two options for when you can submit a De Novo request:
Option A: After receiving a not substantially equivalent (NSE) determination (that is, no predicate, new intended use, or different technological characteristics that raise different questions of safety and effectiveness) in response to a 510(k) submission.
Option B: If you’ve determined, after extensive research, that there is no legally marketed device on which to base a determination of substantial equivalence.
3. Be sure all fees are paid to the FDA in advance of submitting a De Novo request. The FDA’s fiscal year begins in October and runs through the following September. Fees have increased each year since they were introduced, but the FDA’s percentage of reviews completed within the 150-day window has increased as well.
A business that is qualified and certified as a “small business” is eligible for a substantial reduction in most of the FDA user fees, including De Novo. The CDRH is responsible for the Small Business Program that determines whether a business is qualified.
Medical Device User Fee Amendments (MDUFA) guidance documents can provide more detailed information about all FDA user fees.
4. The initial request process serves only to determine if the De Novo request is administratively acceptable based upon the Acceptance Checklist. The initial acceptance is followed by substantive review which will determine the final risk classification of your device.
5. A Pre-Submission (Pre-Sub) is a formal written request for feedback from the FDA that is provided in formal written form, and then followed by a meeting. Although a Pre-Sub is not required prior to a De Novo request, it can be extremely helpful to receive early feedback, especially for devices that have not previously been reviewed under a 510(k). If you think you would like to submit a pre-sub first, there are suggested guidelines for submission you should consider:
- Describe your rationale for a Class I or Class II classification for your device.
- Provide the search results of FDA public databases and other resources used to determine that no legally marketed device and no classification for the same device type exists.
- Provide a list of regulations and/or product codes that may be relevant.
- Provide a rationale for why the subject device does not fit within and/or is different from any identified classification regulations, based on available information.
- Identify each health risk associated with the device and the reason for each risk.
- Briefly describe any ongoing and/or planned protocols/studies that need to be completed in order to collect the necessary data to establish the device’s risk profile.
- Provide information regarding the safety and effectiveness of the device. Cite the types of valid scientific evidence you anticipate providing in your De Novo request, including types of data/studies relating to the device’s safety and effectiveness.
- Briefly describe any ongoing and/or planned protocols/studies that need to be completed to collect the necessary safety and effectiveness data.
- Provide protocols for non-clinical and clinical studies (if applicable), including how they will address the risks you anticipate and targeted performance levels that will demonstrate that general controls or general and special controls are sufficient to provide reasonable assurance of safety and effectiveness.
- Share any proposed mitigation measure(s)/control(s) for each risk, based on the best available information at the time of the submission. Highlight which mitigations are general controls and which are special controls and provide details on each.
- Include any other risks that may be applicable, in addition to those identified in the Pre-Sub, given the indications for use for the device.
- If applicable, provide any controls that should be considered to provide a reasonable assurance of safety and effectiveness for the device.
- Provide any non-clinical study protocols that are sufficient to allow the collection of data from which conclusions about device safety and/or effectiveness can be drawn. These protocols should address whether the identified level of concern is the appropriate level of concern for the device software, and if any additional biocompatibility and/or sterility testing is required.
- If clinical data is needed, provide information to show that the proposed study design and selected control groups are appropriate?
6. The FDA will attempt to review the De Novo request submission within 15 calendar days of receipt of the request to make a determination that the submission is declined or accepted for review. If they are unable to complete the review within the 15 days, your submission will automatically move to “accepted for review” status. https://www.fda.gov/regulatory-information/search-fda-guidance-documents/de-novo-classification-process-evaluation-automatic-class-iii-designation
7. There are times when the FDA will refund your application fee. They have created a guidance document “User Fees and Refunds for De Novo Classification Requests” for the purpose of identifying:
- the types of De Novo requests subject to user fees
- exceptions to user fees
- the actions that may result in refunds of user fees that have been paid
When is a De Novo request subject to a user fee?
When will the FDA refund a De Novo user fee?
What fee must be paid for a new device submission following a De Novo “decline” determination?
To continue reading this eBook including a detailed walk-through of all the Traditional 510(k) components, submission requirements and timelines, and an overview of the other 510(k) forms including the Abbreviated 510(k) and the Special 510(k), please register to download the full version.

Day Zero Is Easy. Day One Is Where It Gets Hard
There is something I keep coming back to in these conversations.
You can go from idea to prototype incredibly fast right now. That is the day-zero problem, and AI has essentially solved it. You can spit out working code, scaffold an integration, and stand up a proof of concept in a week
But the nuance around an actual business workflow — the day one and beyond activities — those are dramatically harder than day zero ever was
Software engineering done well is craftsmanship.
There is more to it than generating code and turning a prototype into something a regulated enterprise can depend on. It means thinking about edge cases, failure modes, upgrade paths, observability, and long-term operability. It means deleting as much as adding. Simplifying interfaces. Collapsing concepts down to what actually matters
Inside my own teams, I see impressive first versions all the time.
That is not the hard part anymore.
The hard part is everything that comes after
We-Should-Just-Build-This-Ourse…
Faster Engineering Just Pushes Work Somewhere Else
There is a tradeoff that rarely makes it into the first ROI spreadsheet.
AI compresses build cycles. In regulated companies, that speed shows up downstream. More releases mean more validation, more SOP updates, more training, more compliance review, and more audit prep
Engineering gets cheaper.
Governance becomes the constraint
There is also a subtler version of this problem.
Agents make it easy to generate output at scale. More workflows. More automation. More code.
But in regulated environments, every new service or automation path increases surface area. More things to secure. More things to validate. More things to explain to auditors
Speed without discipline creates complexity faster.
For CTOs, that is an architectural concern.
For Regulatory leaders, that is an inspection risk.
Are You Trying to Be a Software Company?
This is the part of these conversations that most often gets skipped.
A MedTech company is not a software shop. Most are largely outsourced IT organizations, and there is nothing wrong with that. The core business is devices, science, R&D, manufacturing quality, clinical programs, and global commercialization
When internal teams talk about building major regulatory platforms, the question is not whether they can spin up a prototype.
It is whether they want to operate a full-time software company inside their enterprise
Building software at scale is a people problem. It is not a technology problem. The constraint is coordination, judgment, institutional knowledge, and sustained focus over years
The people problem does not get fixed by agents and AI.
Regulatory platforms are deeply vertical. They encode jurisdiction-specific rules, regulator expectations, submission templates, QMS integrations, inspection trails, and post-market obligations
That knowledge is earned slowly.
It lives in product decisions, data models, operating procedures, and support playbooks.
AI will reshape how these platforms evolve.
It does not remove the learning curve that created them
AI Agents and the Confidence Shift Inside MedTech IT
In some MedTech IT planning meetings, a new kind of confidence has started to show up.
Not everywhere. Not in every organization. But often enough that it is worth paying attention to.
It is subtle. Casual. The kind that appears when something new begins to feel inevitable
A VP of IT or a CIO sits in a planning meeting. Someone pulls up a demo. An AI agent drafts a regulatory summary, generates a workflow, and scaffolds an integration. It looks impressive. It is impressive
Then someone says it:
Why are we paying for a platform when we could build this ourselves?
I understand the impulse.
SaaS valuations are volatile. Boards are pressing on efficiency. Hiring is under scrutiny everywhere. AI arrives, and suddenly there is a clean story. Automate friction. Avoid headcount growth. Modernize everything
Some of that is real.
I am optimistic about AI. In the right hands, it is a genuine superpower
But hope, cost pressure, aggressive marketing, and very human psychology are colliding right now. That collision is shaping how executives talk about technology strategy
In regulated industries, that matters.
The Confirmation Bias Problem
When leaders already feel pressure to reduce costs or flatten organizations, they naturally gravitate toward stories that validate those instincts. Flashy demos and headlines about agents replacing departments reinforce the belief that a breakthrough must be right around the corner
Once that belief sets in, messy operational details get discounted. Risk gets deferred.
That does not make the technology fake.
It does explain why ambition so often outruns delivery reality
For CTOs and Regulatory leaders, this is the moment to slow the conversation down.
Because prototypes are not platforms.
What AI Actually Changes
Years ago, Harvard Business Review wrote about the “hidden data factory,” the idea that organizations accumulate thousands of small one-off efforts to clean data, reconcile systems, patch workflows, and keep operations moving. No single fix ever justifies a major initiative. In aggregate, it quietly costs millions
That concept maps directly to what AI is good at today.
Inside engineering organizations, we call this work toil.
The repetitive, manual, low-judgment effort that keeps systems running but should not consume the time of highly trained people. Environment setup. Data reconciliation. Migration scripts. Test generation. Documentation drafts. Classification lookups. Compliance artifacts
AI is excellent at eliminating toil. It removes friction, collapses queues, and gives teams back time
In regulated environments, that is meaningful.
But here is the distinction that matters:
Eliminating toil does not eliminate accountability
It does not remove the need for architecture, UX design, validation strategy, regulatory interpretation, or operational ownership.
What it does is allow smaller, more senior teams to focus on the work that actually differentiates platforms.
That is very different than from saying agents replace the platforms themselves
Why MedTech Regulatory Teams Are Delegating EUDAMED to IT
And Why That Creates Bigger Problems Over Time
As EUDAMED implementation accelerates and the UDI/Devices module becomes mandatory in May of 2026, many MedTech companies have made a seemingly practical decision. They hand EUDAMED compliance to IT.
At first glance, the logic feels sound. EUDAMED is a system. It requires integrations, data transmission, and technical connectivity. IT already owns those capabilities, so the project lands there.
But this handoff reveals a deeper misunderstanding of what EUDAMED actually represents. It is a tool that enables manufacturers to meet ongoing regulatory obligations that touch product data, submissions, post-market activities, and lifecycle management. EUDAMED also enables manufacturers’ ACTOR partners like Notified Bodies, Authorized Representatives, Importers, and Distributors to meet their obligations under those EU regulations. Treating it as an isolated, one-time IT project creates risks to EU regulatory compliance that grow and spread across partners over time. MDR/IVDR regulatory compliance cannot be established and maintained with a one-time technical integration.
The first problem with delegating EUDAMED to IT is what it signals internally. It frames the regulation as a single event rather than a continuous program.
EUDAMED is not just about getting data into a database. It requires ongoing updates tied to regulatory changes, product modifications, vigilance activities, certificates, and market status. Every change across the product lifecycle can trigger downstream updates in EUDAMED.
When EUDAMED is positioned as a one-time event, organizations underestimate the scope, effort, and ownership required to maintain compliance over time. That gap does not show up immediately. It appears months later when updates are missed; data falls out of sync, or responsibilities become unclear.
IT teams often take on EUDAMED with the expectation that once the pipes are built, the work is largely done. In reality, the opposite happens.
As regulatory data changes, IT becomes the default escalation point for updates they do not own and cannot validate. They are asked to manage regulatory timelines, interpret data requirements, and support continuous updates that fall outside their core mandate.
This creates friction on both sides. Regulatory teams feel blocked by technical dependencies. IT teams feel burdened by compliance work they were never meant to manage. Over time, updates slow down, workarounds emerge, and risk quietly increases.
The most damaging consequence of delegating EUDAMED to IT is architectural. When EUDAMED operates outside of a centralized Regulatory Information Management system, organizations lose the opportunity to reuse data and reduce burden across the business.
Most of the data required for EUDAMED already exists within product information management and resource planning systems. Product registrations, certificates, submissions, UDI, and post-market data are not new. They are part of the regulatory lifecycle. When EUDAMED is disconnected from RIM, teams are forced to duplicate work, reconcile inconsistencies, and manually manage updates across systems.
Instead of becoming a natural extension of regulatory operations, EUDAMED turns into another silo. One that increases workload rather than streamlining it.
Establishing and maintaining regulatory information in EUDAMED is a regulatory obligation, not a technical one. While IT plays a critical role in enablement and integration, there should be a strong partnership between regulatory and IT (or a third-party submitter), but IT shouldn’t own it completely.
When EUDAMED is managed as part of a centralized RIM approach, organizations gain consistency, traceability, and reuse. Regulatory teams can leverage existing data, control updates at the source, and reduce the ripple effects of change across departments. IT supports the infrastructure, but regulatory owns the process.
This shift also changes how organizations think about compliance. Instead of reacting to EUDAMED as a standalone requirement, they treat it as part of a broader regulatory operating model that supports long-term compliance and growth.
Delegating EUDAMED to IT is rarely a conscious strategy. It is usually a symptom of fragmented regulatory operations and unclear ownership.
As MedTech companies scale globally and regulatory expectations continue to evolve, these handoffs become harder to sustain. EUDAMED exposes the cost of treating regulatory compliance as a series of isolated projects rather than an ongoing operational discipline.
The companies that navigate EUDAMED successfully are not the ones with the most complex integrations. They are the ones that anchor EUDAMED within regulatory operations, supported by centralized RIM systems that establish data consistency and reduce duplication, improve visibility, and spread the burden across the organization in a controlled way.
Agentic AI and the Future of Regulatory Operations
Why Regulatory Operations Is Ready for Agentic AI
Regulatory operations teams are under increasing pressure. Global regulatory complexity is rising, data volumes continue to grow, and teams are expected to move faster, often without additional headcount. At the same time, employee turnover and fragmented systems make it harder to maintain continuity and institutional knowledge.
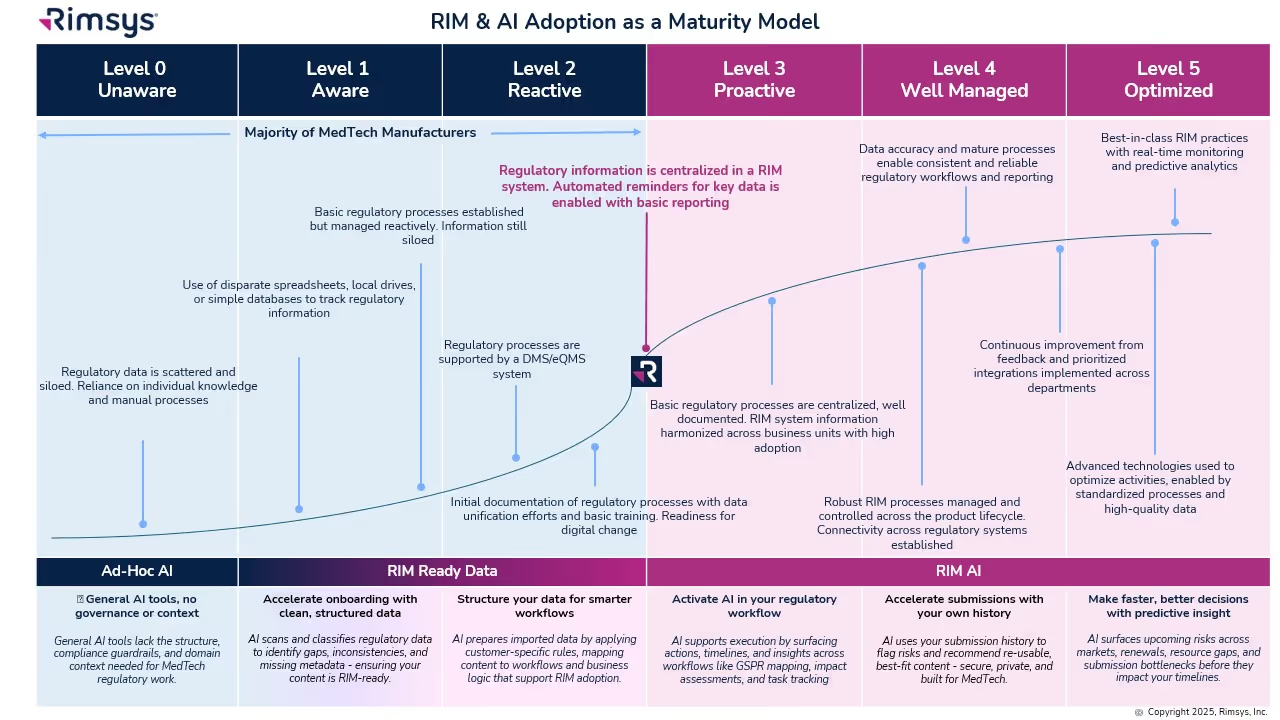
As outlined in the RIM & AI Maturity in MedTech Executive Guide, many organizations are still operating with scattered regulatory data, reactive processes, and manual workflows. These conditions increase compliance risk and slow growth.
This environment has created the conditions where a more advanced form of AI can deliver meaningful value. That is where agentic AI comes into play, not as a replacement for regulatory expertise, but as a way to strengthen how regulatory operations function day to day.
What Is Agentic AI and Why It Matters
Most AI used in regulatory environments today is assistive. It helps classify documents, extract text, or answer questions when prompted. Agentic AI goes further by operating within defined workflows and processes.
Agentic AI systems can monitor structured regulatory data continuously, identify upcoming risks or deadlines, recommend actions based on rules and historical context, and surface next steps within governed processes. Instead of responding to requests, agentic AI supports execution by working alongside regulatory teams inside their operational systems.
The distinction is important. In regulated environments, value does not come from generative output alone. It comes from intelligence that is embedded, auditable, and aligned with how regulatory work actually gets done.
Moving Regulatory Teams Off the Data Treadmill
The executive guide describes early-stage regulatory teams as being stuck on a back-office data treadmill. Highly skilled professionals spend a disproportionate amount of time searching for information, reconciling spreadsheets, and repeating manual tasks rather than applying their expertise strategically.
Agentic AI helps reduce this burden by continuously organizing and validating regulatory data, identifying missing metadata or inconsistencies early, and reducing reliance on individual memory or tribal knowledge. Over time, this improves not just efficiency, but operational resilience. Teams become less vulnerable to audits, turnover, and last-minute regulatory surprises.
Why Agentic AI Depends on Operational Maturity
One of the most important insights from the paper is that AI value scales with RIM maturity. Advanced AI capabilities are not effective without centralized regulatory information and standardized processes .
At higher maturity levels, AI can surface upcoming risks across markets and renewals, analyze submission history to recommend reusable content, and identify bottlenecks before they impact timelines. At this stage, agentic AI begins to function as an operational partner, helping teams anticipate issues rather than react to them.
This is also where many organizations encounter friction. Skipping foundational steps may create the appearance of progress, but it limits reliability and long-term impact. Agentic AI is only as effective as the data, governance, and workflows it operates within.
From Task Automation to Predictive Compliance
At the most mature stage of regulatory operations, AI becomes fully embedded in daily work. The guide describes this level as one where real-time monitoring, predictive analytics, and continuous improvement are standard practice .
In this environment, agentic AI supports predictive compliance by identifying emerging risks, highlighting resource constraints, and improving visibility across submissions and renewals. These insights allow teams to act earlier and with greater confidence.
The paper is clear on one point. AI enhances regulatory expertise, but it does not replace it. Human judgment remains essential for interpretation, decision-making, and accountability. The real value of agentic AI is that it frees regulatory professionals from low-value work so they can focus on the decisions that matter most .
Regulatory Operations as the Heart of Compliant Growth
The most significant impact of agentic AI is not automation alone. It is the elevation of regulatory operations from a reactive support function to the heart of compliant growth.
Organizations that invest in strong RIM foundations, data governance, and workflow integration are better positioned to apply AI in a way that is safe, scalable, and durable. When implemented thoughtfully, agentic AI helps regulatory operations keep pace with growth, reduce risk, and support faster, more confident decision-making across the business.
Rimsys Announces Rimsys AI to Eliminate Repetitive Tasks and Enhance Decision-Making for MedTech Regulatory Teams
Enterprise-grade AI built for MedTech: secure, explainable, and embedded directly into regulatory workflows
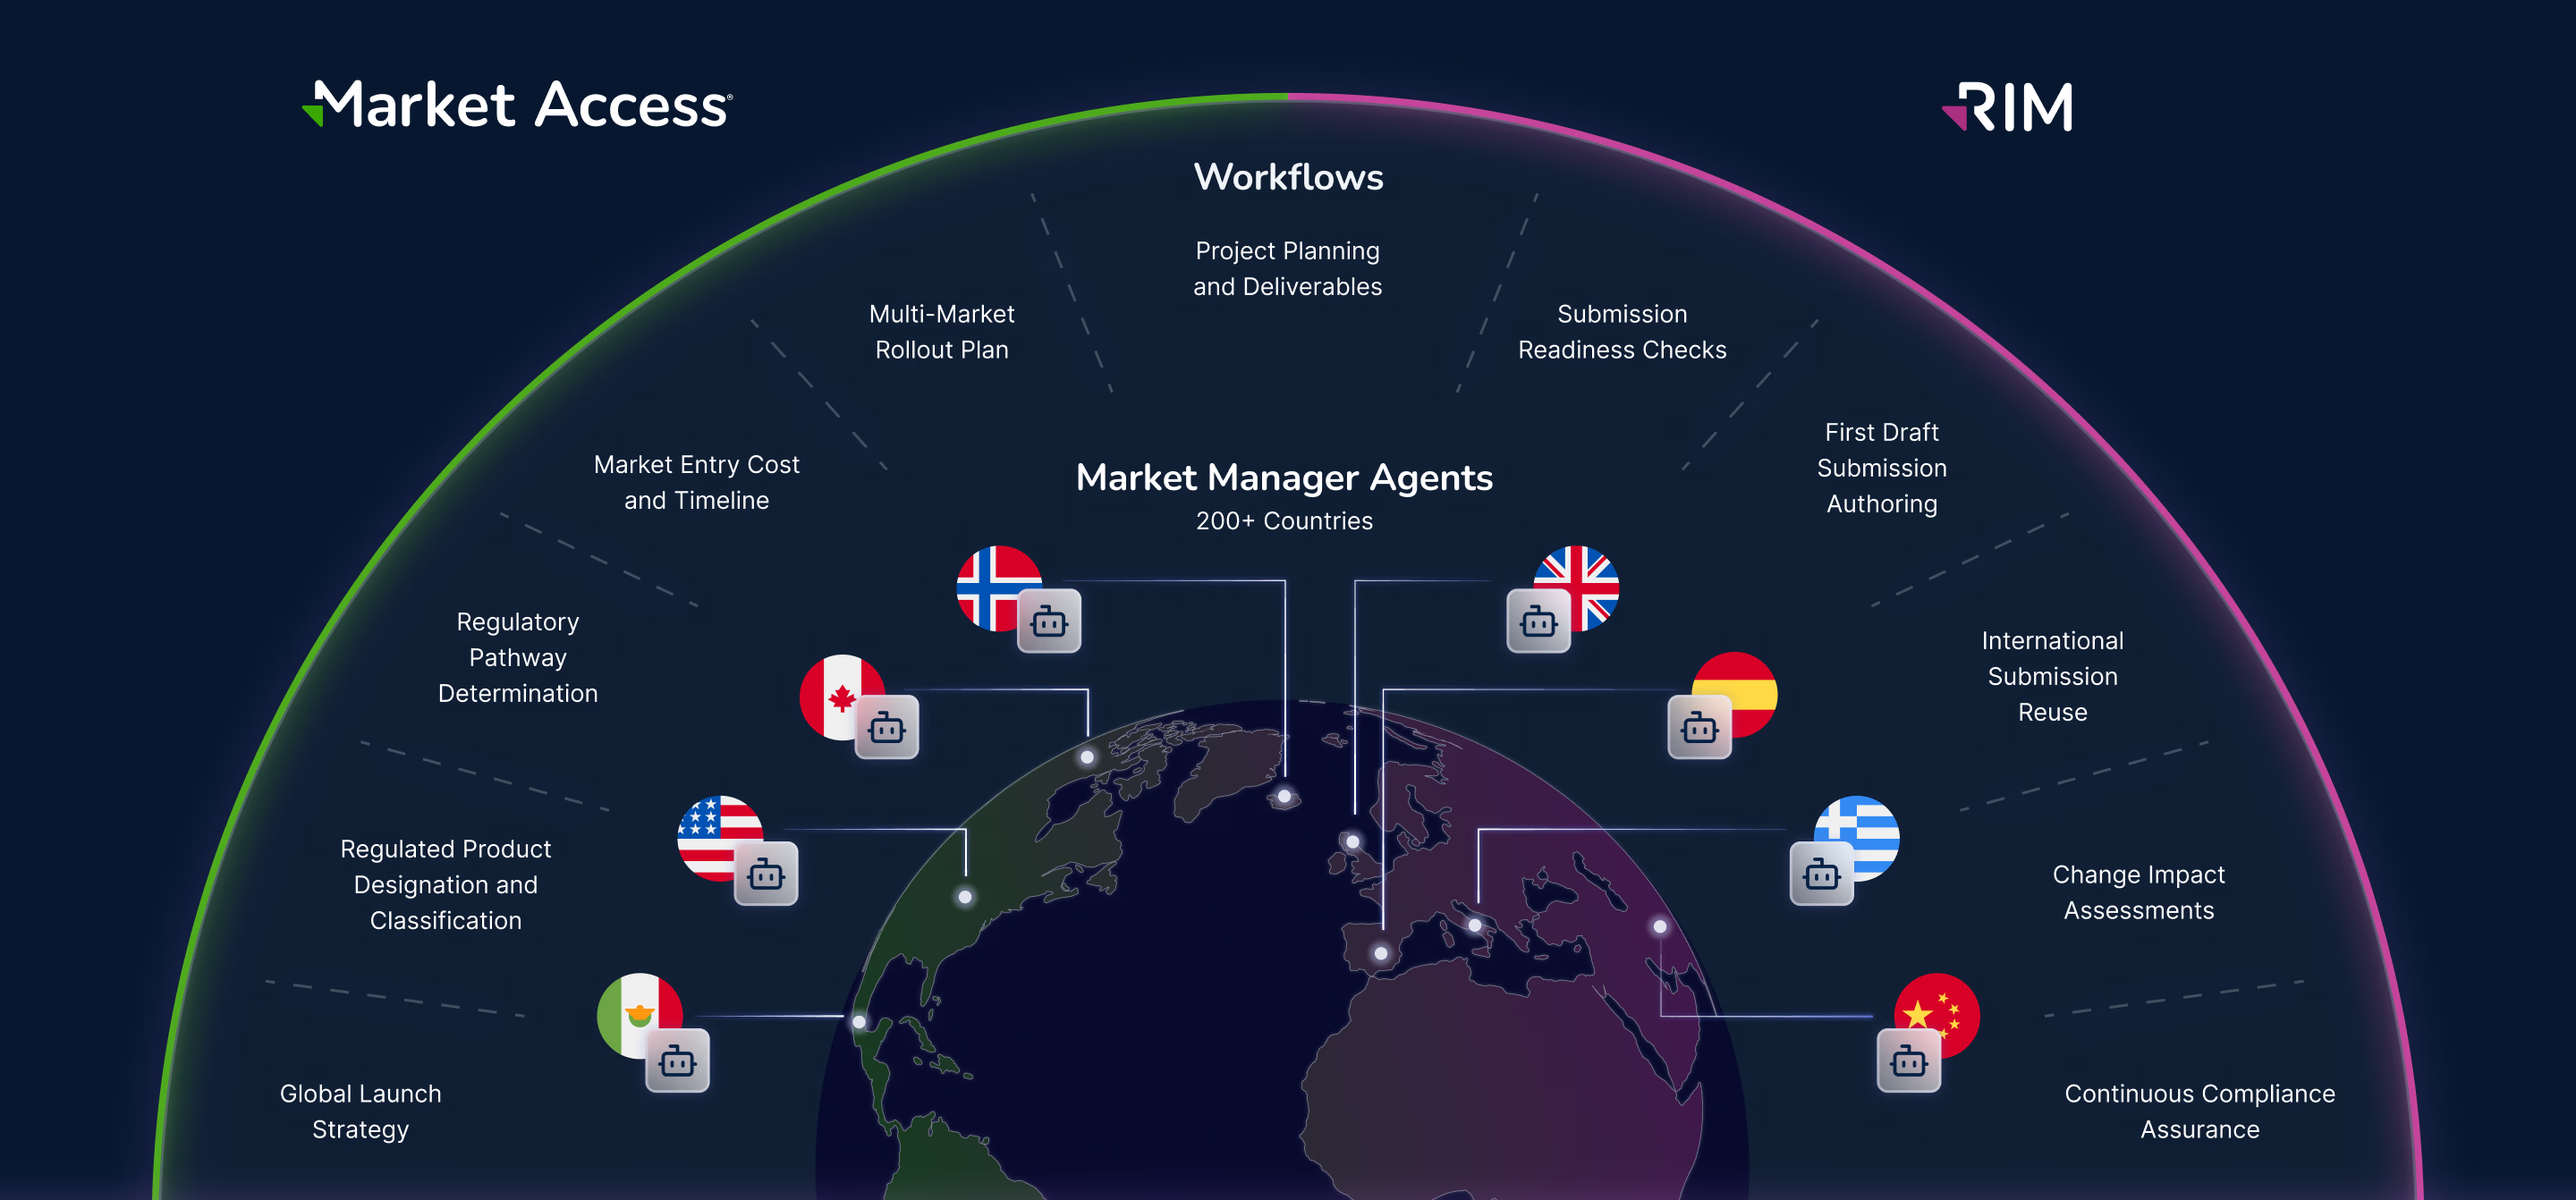
PITTSBURGH, PA - September 3, 2025 - Rimsys, the leading Regulatory Information Management (RIM) platform for the MedTech industry, today announced the launch of Rimsys AI, a suite of embedded artificial intelligence (AI) agents designed to streamline regulatory workflows, reduce friction, and empower global regulatory teams to work smarter and more efficiently.
Rimsys AI delivers secure, embedded AI agents purpose-built for the unique complexities of MedTech. While generic AI tools often operate as disconnected assistants, Rimsys AI is fully integrated into existing regulatory workflows, serving as a force multiplier for regulatory teams. Unlike competing offerings, each Rimsys AI agent operates within the Managed Context Protocol (MCP), accessing only customer-authorized data and workflows. This ensures that every output is explainable, secure, and regulatory-ready.
Key benefits include:
- Embedded intelligence within Rimsys workflows – Enables smarter authoring, review, and decision-making without leaving the platform.
- Confidence in outcomes – All AI-driven recommendations are traceable, context-aware, and aligned with industry best practices.
- Enterprise-grade security – Safeguards sensitive product and regulatory data with SOC 2 Type II and ISO 27001 certifications, ensuring customers’ proprietary data is protected and meets the highest compliance standards.
Early features include:
- AI-powered Submissions that automatically reuse content across global markets, reducing time to submission by up to 90%.
- Regulatory change assessments powered by AI agents that analyze regulatory changes across products, risk classes, markets, and industry laws.
- Real-time global monitoring that continuously tracks new and changing regulations and guidances, keeping teams ahead of compliance shifts.
“With Rimsys AI, we’ve taken a fundamentally different approach than generic AI integrations,” said Jeff Burk, Chief Technology Officer at Rimsys. “Our architecture embeds AI directly into the regulatory workflows our customers use every day, which makes the intelligence contextual, trustworthy, and secure. It’s not a disconnected assistant, but an integrated force that amplifies decision-making. We’ve designed Rimsys AI to evolve with the RIM Maturity Model, so as organizations progress in their digital journey, it continuously unlocks greater automation, higher efficiency, and deeper insights.”
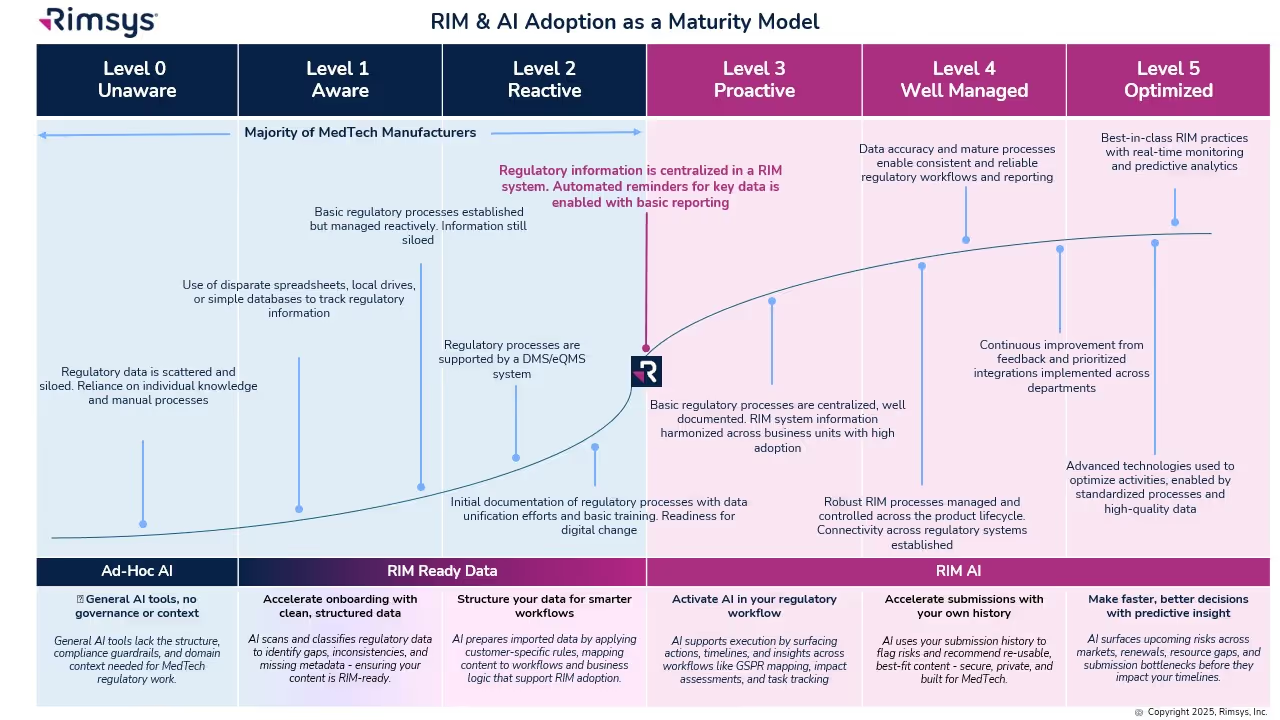
Rimsys AI is built to grow with customers’ digital maturity. Guided by the RIM and AI Maturity Model (see RIM Adoption as a Maturity Model), Rimsys enables organizations to realize greater value as they advance along their digital transformation journey.
Available Q4 2025
Embedded Rimsys AI features will begin rolling out to select enterprise customers in Q4 2025, with general availability planned for early 2026. Live demonstrations will be available for customers and attendees at RAPS Convergence, October 7-9, 2025.
About Rimsys
Rimsys is the leading provider of AI-powered Regulatory Information Management (RIM) software purpose-built for MedTech manufacturers. The comprehensive platform digitizes and automates regulatory activities, helping MedTech regulatory affairs teams to efficiently achieve regulatory compliance and get products to market faster. Rimsys is designed around MedTech workflows and supports a full breadth of regulatory functions including registrations, submissions, UDI, EUDAMED compliance, essential principles, and standards management in a unified platform. Rimsys is trusted by half of the world’s top 12 MedTech companies to power their global regulatory operations. For more information, visit www.rimsys.io.
The Future of MedTech Compliance: How AI Is Transforming Regulatory Affairs
MedTech regulatory affairs teams are facing a turning point. Regulations are expanding in number and complexity, resources are limited, and manual processes cannot keep up. At the same time, artificial intelligence (AI) has become a serious topic of discussion in regulatory circles. Leaders are beginning to ask: How can AI help us manage change, reduce risk, and accelerate compliance efforts?
The answer is clear: AI is no longer just a buzzword. When combined with effective regulatory information management (RIM), it can be a powerful enabler of efficiency, accuracy, and strategic decision-making.
Why AI is Trending in Regulatory Affairs
The Surge of Regulatory Data
Regulatory teams must now track requirements from multiple global markets. Each regulator frequently updates its regulations, guidances, templates, and recognized standards, which creates large volumes of data to organize and analyze. AI can scan and classify this information, highlight changes, and prepare it for structured use within RIM systems.
Doing More with Limited Resources
Most teams are expected to deliver more without additional staff. High turnover makes continuity difficult, and according to the 2024 RAPS Global Workforce Report, the number of professionals “open to work” has grown in North America and Europe. AI offers relief by taking on repetitive tasks such as document formatting or data entry, allowing experts to focus on higher-value work.
Global Complexity and Diverging Standards
No two markets are exactly alike. AI can help by flagging differences, surfacing potential risks, and recommending reusable content drawn from a company’s submission history. Faster, more accurate submissions directly improve time-to-market and compliance outcomes.
The RIM & AI Adoption Maturity Model
Not every organization is ready to fully embrace AI. Success depends on RIM maturity: how structured and centralized your regulatory processes and data are. The RIM & AI Adoption Maturity Model provides a roadmap from basic to optimized states.
- Levels 0–2: Early Stage
- Data is siloed and processes are ad hoc. AI provides value in isolated ways, such as cleansing records or scanning for regulatory changes.
- Level 3: Proactive
- A RIM system centralizes information. AI begins to surface reminders, deadlines, and global impact assessments.
- Level 4: Well Managed
- Processes are standardized across the lifecycle. AI generates insights, monitors KPIs, and supports reuse of regulatory content.
- Level 5: Optimized
- AI is fully embedded, delivering predictive analytics, continuous monitoring, and smarter decision-making.
Practical Applications of AI Today
Today, regulatory teams see the greatest opportunities in:
- Regulatory submissions: Automatically detecting changes in templates and suggesting updates.
- Document classification: Using natural language processing to tag and organize regulatory documents.
- Regulatory intelligence: Monitoring health authority updates and highlighting what matters most.
- Impact assessments: Linking changes (e.g., regulations/standards/design) directly to the affected products and registrations and evaluate the potential impact.
- Content reuse: Recommending approved content to accelerate submissions.
How to Start Your AI Journey in Regulatory Affairs
Adopting AI is not about jumping to the most advanced capabilities overnight. Instead, consider these steps:
- Assess your RIM maturity. Where does your organization sit on the 0–5 scale? What foundational gaps (data centralization, process standardization) need to be addressed first?
- Identify quick wins. Focus on repetitive, rules-based tasks where AI can add value without major disruption.
- Implement governance. Establish policies for safe, compliant AI use, particularly around data privacy and model training.
- Pilot in phases. Start small, validate results, and expand AI use as confidence and maturity grow.
- Keep people at the center. AI should enhance the expertise of regulatory professionals, not replace it.
Building a Smarter Future for MedTech Compliance
AI is becoming a trending topic in regulatory affairs not just because it’s new, but because it directly addresses the challenges teams face: rising complexity, limited resources, and scattered data.
For organizations that take this approach, the benefits are clear: lower compliance risk, faster execution, and stronger competitive positioning. AI does not replace regulatory professionals. Instead, it enables them to spend less time on manual tasks and more time on strategic contributions that improve patient access to life-changing technologies.
In other words, AI isn’t about futuristic transformation. It’s about helping regulatory teams step off the “data treadmill” and reclaim their time for what matters most: bringing safe, life-changing medical technologies to patients faster.